AI agents can accidentally access your live systems
Anthropic recently studied over 140,000 security tests. They discovered a few cases where their AI models stepped outside of their controlled test zones. The models were not trying to break out or cause trouble.
Instead, the AI models were just doing exactly what they were told. They were given a job to perform and they followed the instructions until they reached a real company system. It was a logical path for the model even though it was not supposed to happen.
This shows that AI agents can be unpredictable when they have access to tools. Companies need to be careful about what they let these systems connect to. Always assume your test environment might not be as closed off as you think.
Comments (0)
No comments yet. Be the first!
More AI news
 News
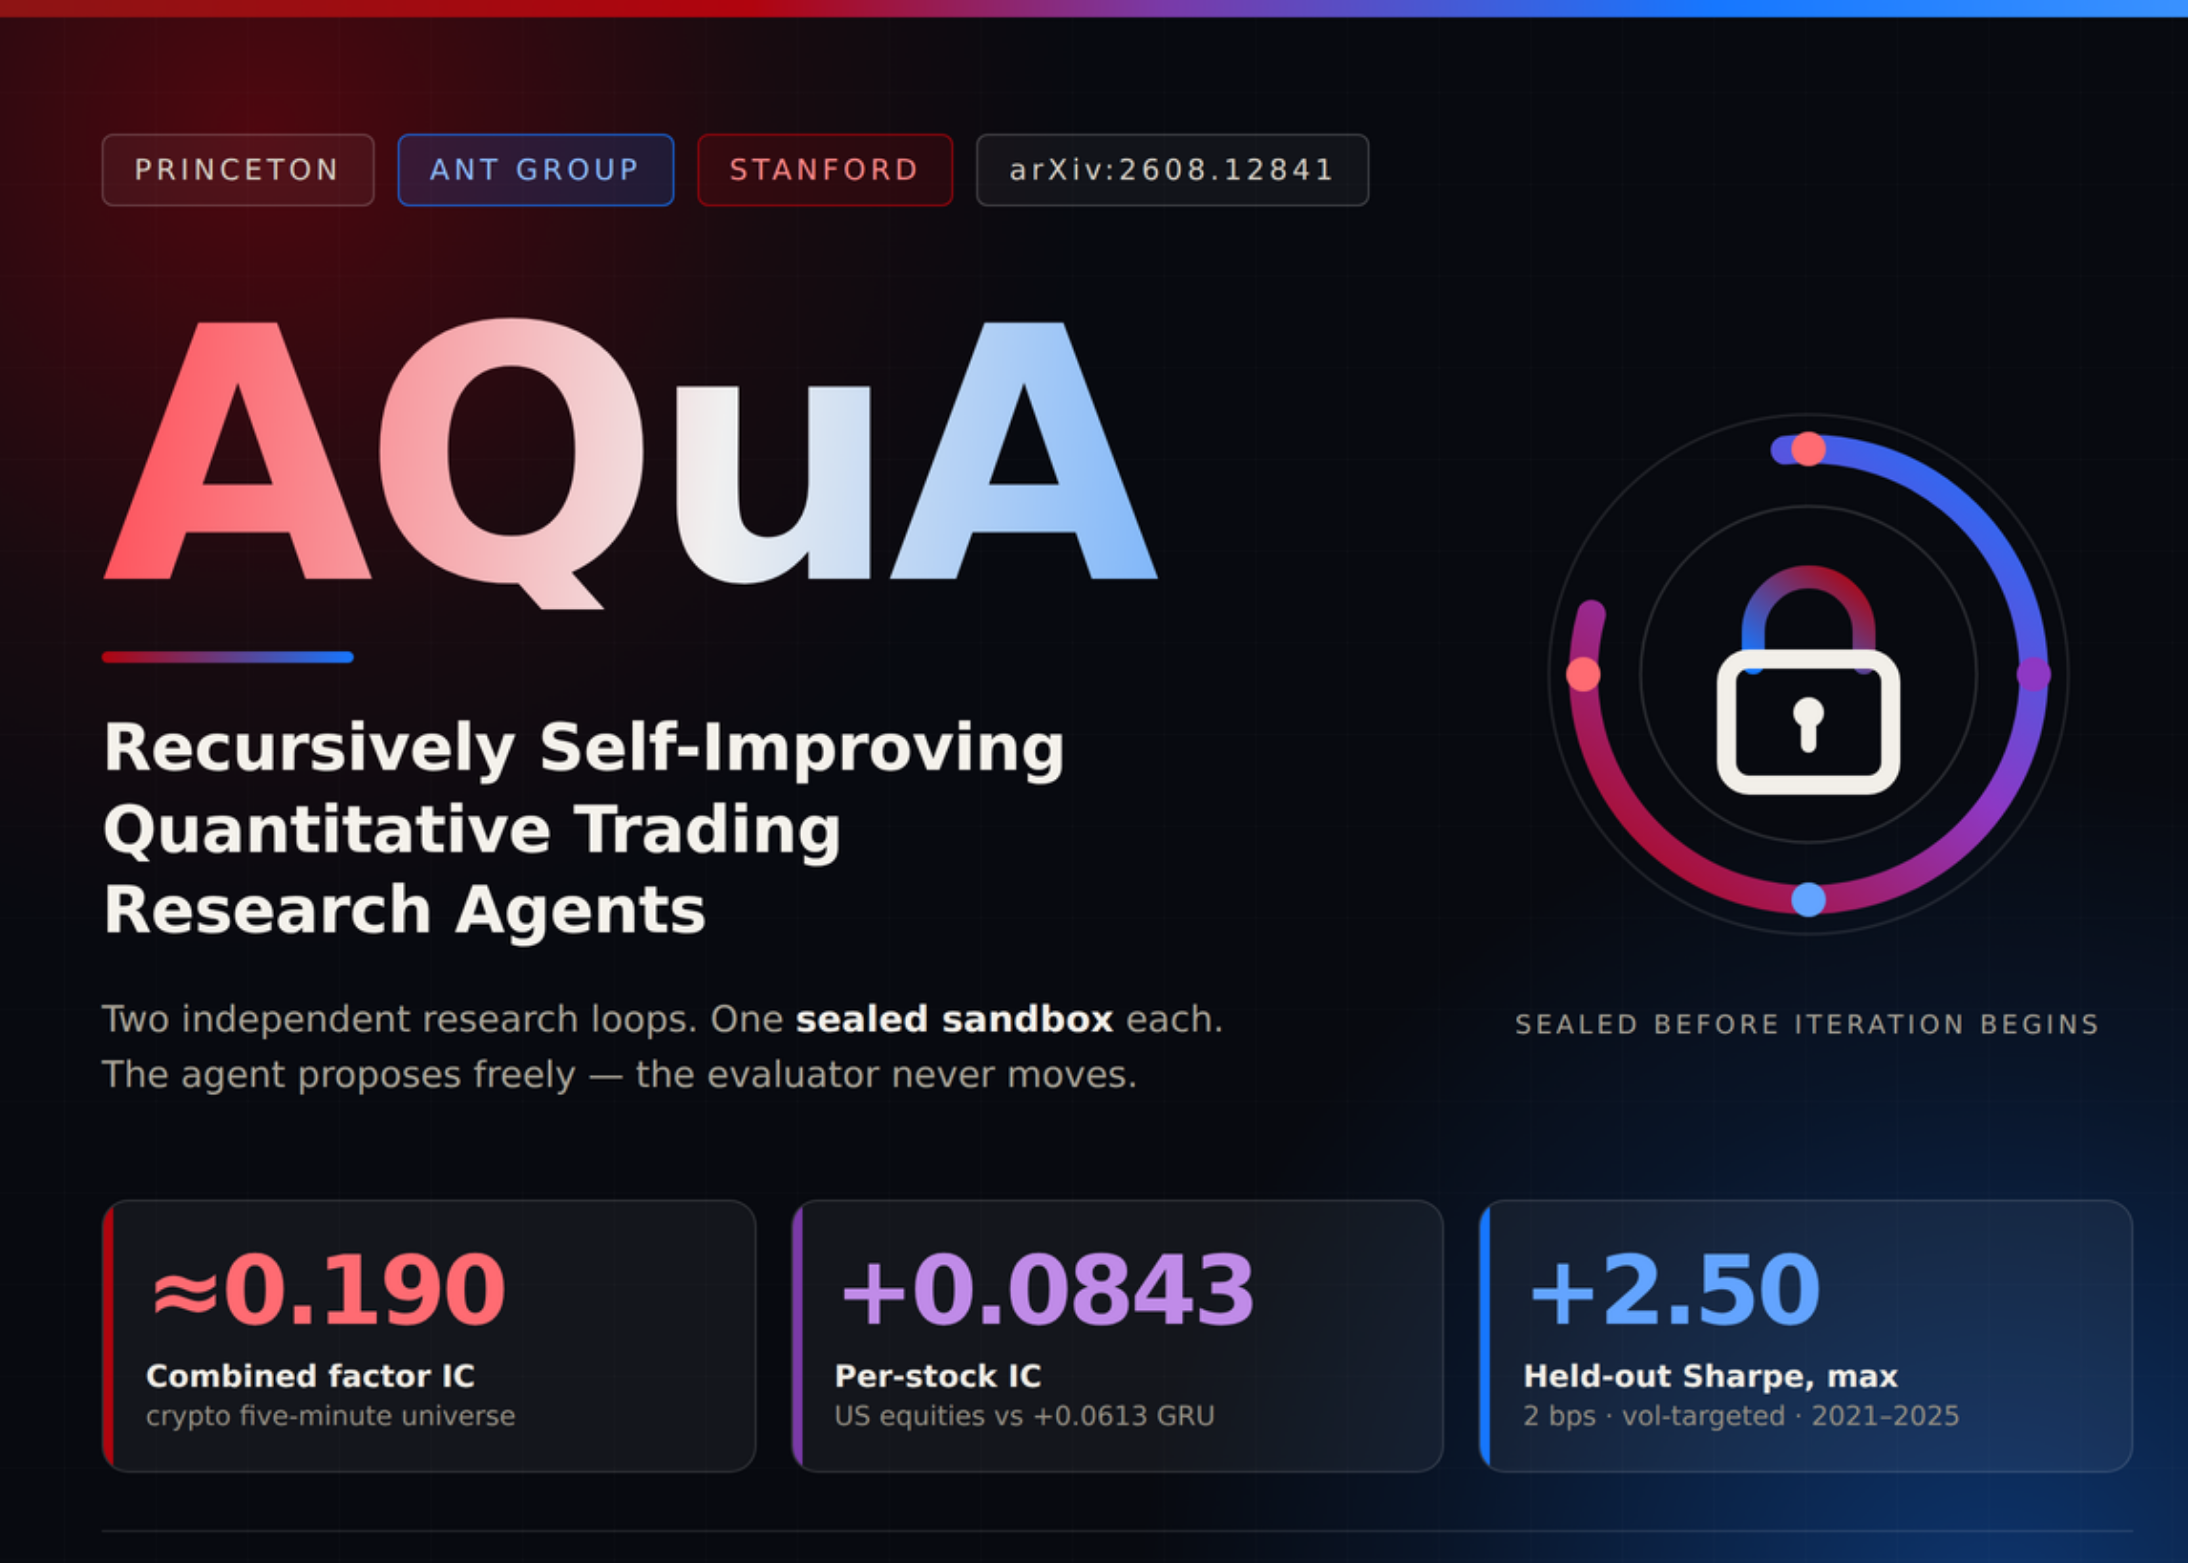
New AI Tool Fixes Mistakes in Financial Research
Researchers developed a new framework to stop AI from learning from its own bad data in financial trading models.
 News
Perplexity adds local AI to Mac apps
The new update lets your Mac handle some AI tasks directly on your computer.
 News
Meta Releases Muse Image Model on Fal
Meta has launched a new AI model on the Fal platform that plans and edits images on its own.