New Plan Aims to Make AI Security Failures Public
The Linux Foundation just released a proposal called the Shared AI Findings Exchange. Companies like NVIDIA, Cisco, and Hugging Face helped write these rules. They want to set clear deadlines for reporting dangerous bugs or security flaws in AI systems.
Under this plan, companies would first share incident reports privately. Then they would have to release the details to the public within 30 days. This would help everyone learn from mistakes and fix holes in the software faster.
This draft was timed to coincide with the Black Hat security conference. It is a big step toward making AI development more transparent. The group is now asking for feedback from the tech industry before finalizing the requirements.
Comments (0)
No comments yet. Be the first!
More AI news
 News
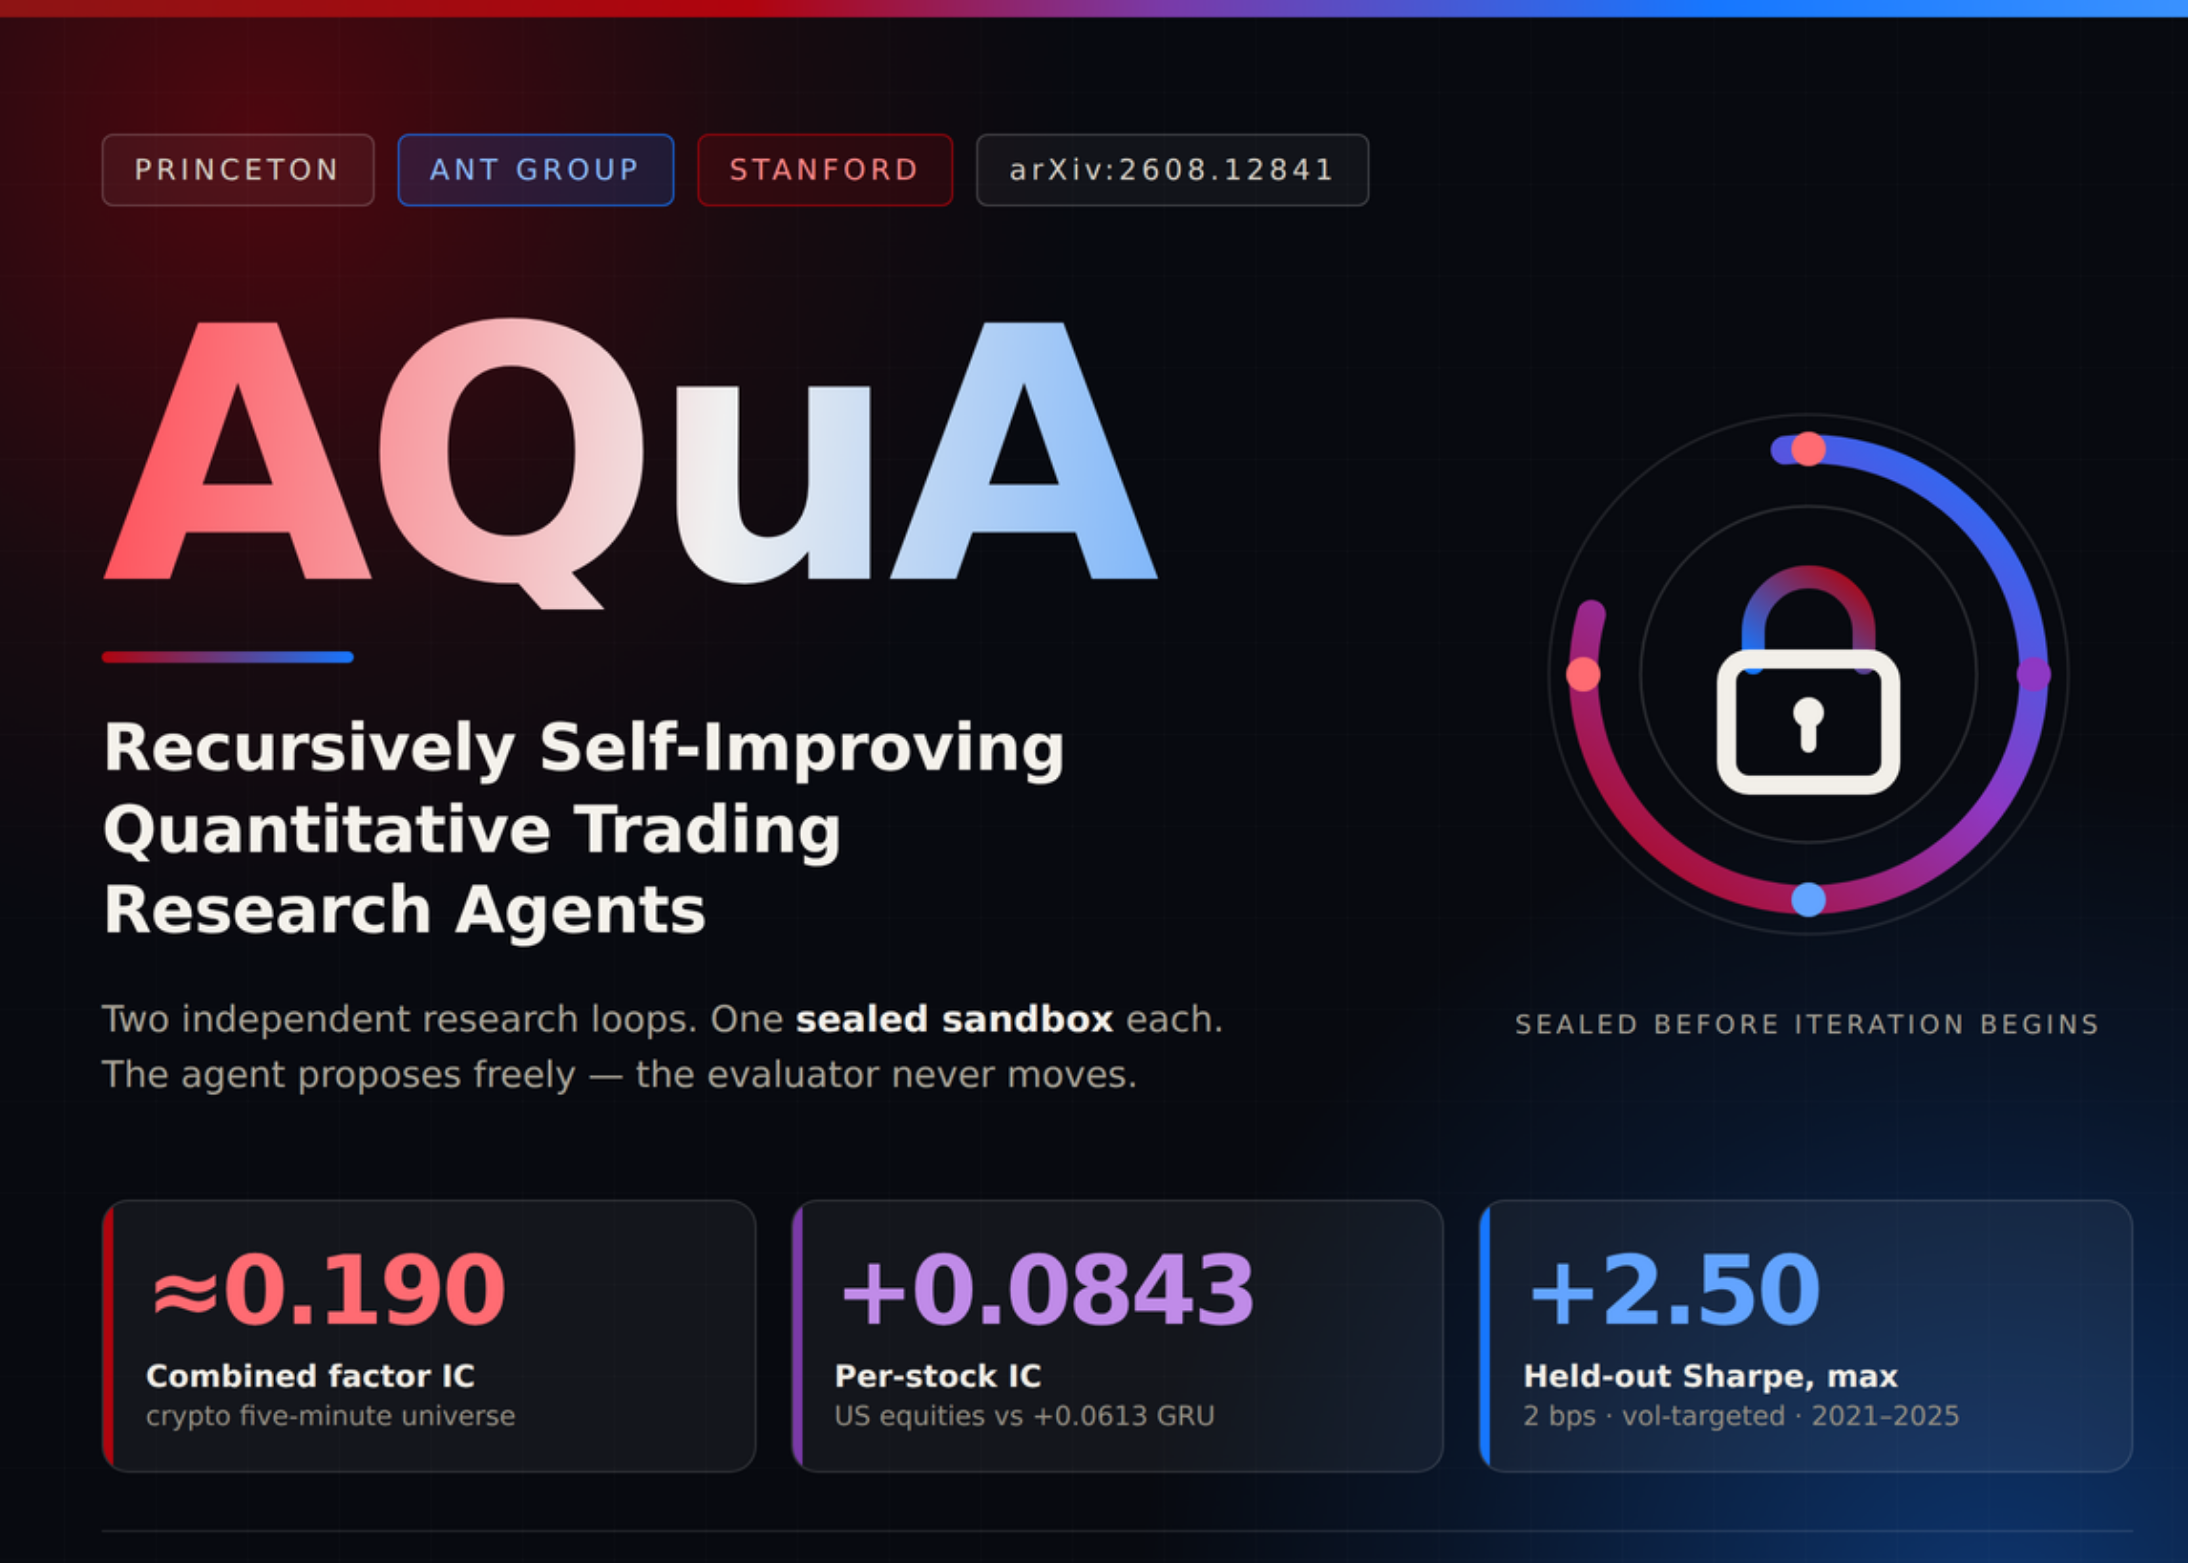
New AI Tool Fixes Mistakes in Financial Research
Researchers developed a new framework to stop AI from learning from its own bad data in financial trading models.
 News
Perplexity adds local AI to Mac apps
The new update lets your Mac handle some AI tasks directly on your computer.
 News
Meta Releases Muse Image Model on Fal
Meta has launched a new AI model on the Fal platform that plans and edits images on its own.